
The local-first API security client
Find the flaws
before they do.
Ryft is a local-first API security testing desktop app for Windows, macOS and Linux that pulls hidden API endpoints out of a web app's JavaScript, reconstructs an OpenAPI spec, and runs multi-credential BOLA/IDOR with negative controls plus the OWASP API Top 10 — entirely on your machine, zero telemetry, no cloud, no account.
Ryft reads the client's JavaScript, learns the API from live traffic, reconstructs a testable spec, and proves broken authorization with multi-credential BOLA — plus an honest OWASP API Top 10 scanner, an intercepting proxy, and a CI-ready CLI. It runs on your machine — your test traffic, captured data, and findings never leave it: no account, no analytics on your testing.
Effortless to drive. Deep by default. Built for APIs.
Why Ryft
What does Ryft find that your other tools miss?
Most scanners replay a request list and grep the responses. Ryft reads the client, learns the API, and tests authorization the way an attacker actually does.
Global Session
Test everything as a logged-in user. Define your login once — Ryft runs it, extracts the token, and carries an authenticated context into every tool. Tokens stay scope-gated to in-scope hosts, and Ryft re-auths on its own when they expire, so short-lived sessions never stall a scan.
JavaScript intelligence
Ryft reads the client. It parses and de-obfuscates front-end JS bundles to surface hidden endpoints, parameters, and leaked secrets your proxy never sees — attack surface most tools walk right past.
Proxy intelligence
More than a man-in-the-middle. As traffic flows, Ryft infers routes, auth schemes, and object relationships on the fly — so you start from a live model of the API, not a flat request log.
Reconstruction & rebundling
No spec? Ryft builds one. It fuses captured traffic with the JavaScript it decoded to rebundle scattered calls into a complete, testable API map you can attack.
Multi-credential BOLA
The #1 API risk, tested honestly. Load several identities at once and Ryft replays every object across each credential set — proving whether one user can reach another's data instead of guessing.
Flows
Chain requests into repeatable sequences — log in, act, verify — then replay the whole flow as a different identity. Ryft exposes the multi-step business-logic and authorization bugs single-request scanners never reach.
Cruise Control
Scan while you browse. Put your targets in scope, turn on the proxy, and just click around the app — Ryft auto-scans every new in-scope request in the background at the intensity you choose (Light → Heavy), non-destructive by default. A live HUD counts what it's seen, probed, and found.
Intercepting proxy & repeater
A full HTTP/HTTPS man-in-the-middle. Capture, pause, edit, and replay traffic from any client or browser.
Honest OWASP API Top 10 scanner
Oracle-backed active checks across the 2023 API Top 10, with FIRM-vs-TENTATIVE confidence — findings you can trust, not false-positive noise.
SideCar fuzzer & JWT Lab
Drive params, headers, and bodies with wordlists and diff responses fast. Decode, tamper, and re-sign JWTs to test alg confusion and weak secrets.
GraphQL testing
First-class GraphQL support — introspect the schema, surface hidden types and fields, and probe queries and mutations for authorization and injection flaws.
AutoPilot
Bring your own key. Get payload ideas, response triage, and plain-English explanations from your own AI provider — your prompts and data never pass through us.
See it in action
What does a real Ryft scan look like?
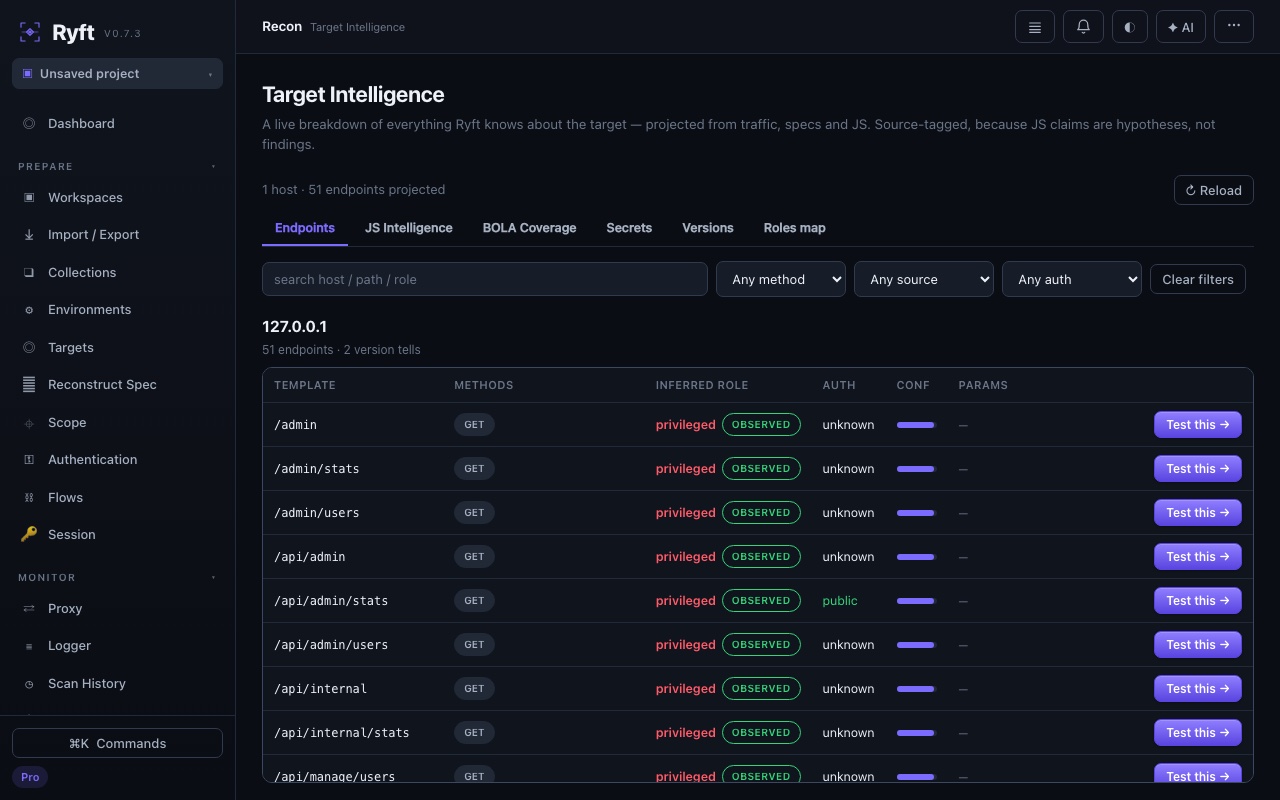
Watch Ryft reconstruct an API from a JavaScript bundle below — then every screenshot is a real scan of a live API: the honest severity breakdown, the evidence behind each finding, and the live map it builds of the target. Click any shot to open it full-size.


About
Who builds Ryft?
Ryft comes from a hacker with 400+ validated API vulnerabilities across U.S. federal government programs. Every check, default, and shortcut in the app earned its place on real targets — the tools that decode the client, learn the API, and prove broken authorization are the ones its author reached for every day, sharpened and put in one place.
What you get
What do you get with a Ryft license?
No tiers, no seats, no per-scan fees. Every capability — the full engine — unlocked with a single license for a full year.
- JavaScript intelligence & endpoint discovery
- Proxy that learns the API as you test
- Spec reconstruction & rebundling from traffic + JS
- Multi-credential BOLA & authorization testing
- Flows — replay request sequences across identities
- Cruise Control — auto-scan in-scope traffic as you browse
- Honest OWASP API Top 10 scanner
- SideCar fuzzer, JWT Lab & GraphQL
- AutoPilot (bring your own key) & full reports
How it works
How do you get started with Ryft?
- 1
Get your license
Pick up a Ryft license — one year of the entire app, no tiers to decode.
- 2
Download
Grab the build for macOS, Windows or Linux. No account, no installer bloat — just the app.
- 3
Activate & attack
Paste your key into Settings → License, point Ryft at your target, and start testing — the whole app unlocks the moment your key is in.
Does Ryft send your data to the cloud?
Ryft runs entirely on your machine. Your API traffic, captured data, and findings never leave your box — no account, no analytics on your testing. The only network call Ryft makes is an anonymous version check on launch: no identifiers, no license key, no test data — nothing else.
FAQ
Common questions about local-first API security testing
Is there a local API security tool that doesn't send data to the cloud?
Yes — Ryft. Ryft is a local-first API security testing desktop app for Windows, macOS and Linux. It runs entirely on your machine, with no cloud, no account and zero telemetry — your targets, traffic and findings never leave your device.
How do I find hidden API endpoints in a web app?
Ryft pulls hidden, undocumented API endpoints out of a web app's JavaScript bundles — source-tagged — and reconstructs a testable OpenAPI spec from the discovered client code, so you can test the real attack surface without any existing docs.
What tool runs the OWASP API Top 10 locally?
Ryft runs the full OWASP API Top 10 on your own machine, across REST and GraphQL, with an honest confidence label on every finding — no cloud, no account, zero telemetry.
Does Ryft need an account or an internet connection?
No. Ryft is local-first and license-only: you activate it with a signed key and test entirely offline. The only network call it makes is an anonymous version check on launch — no identifiers, license key or test data ever leave your machine.
Ready to find what others miss?
Decode the client, learn the API, and prove real authorization flaws — all on your own machine.